Risk Management Framework: Essential Controls and Implementation Strategies for 2026
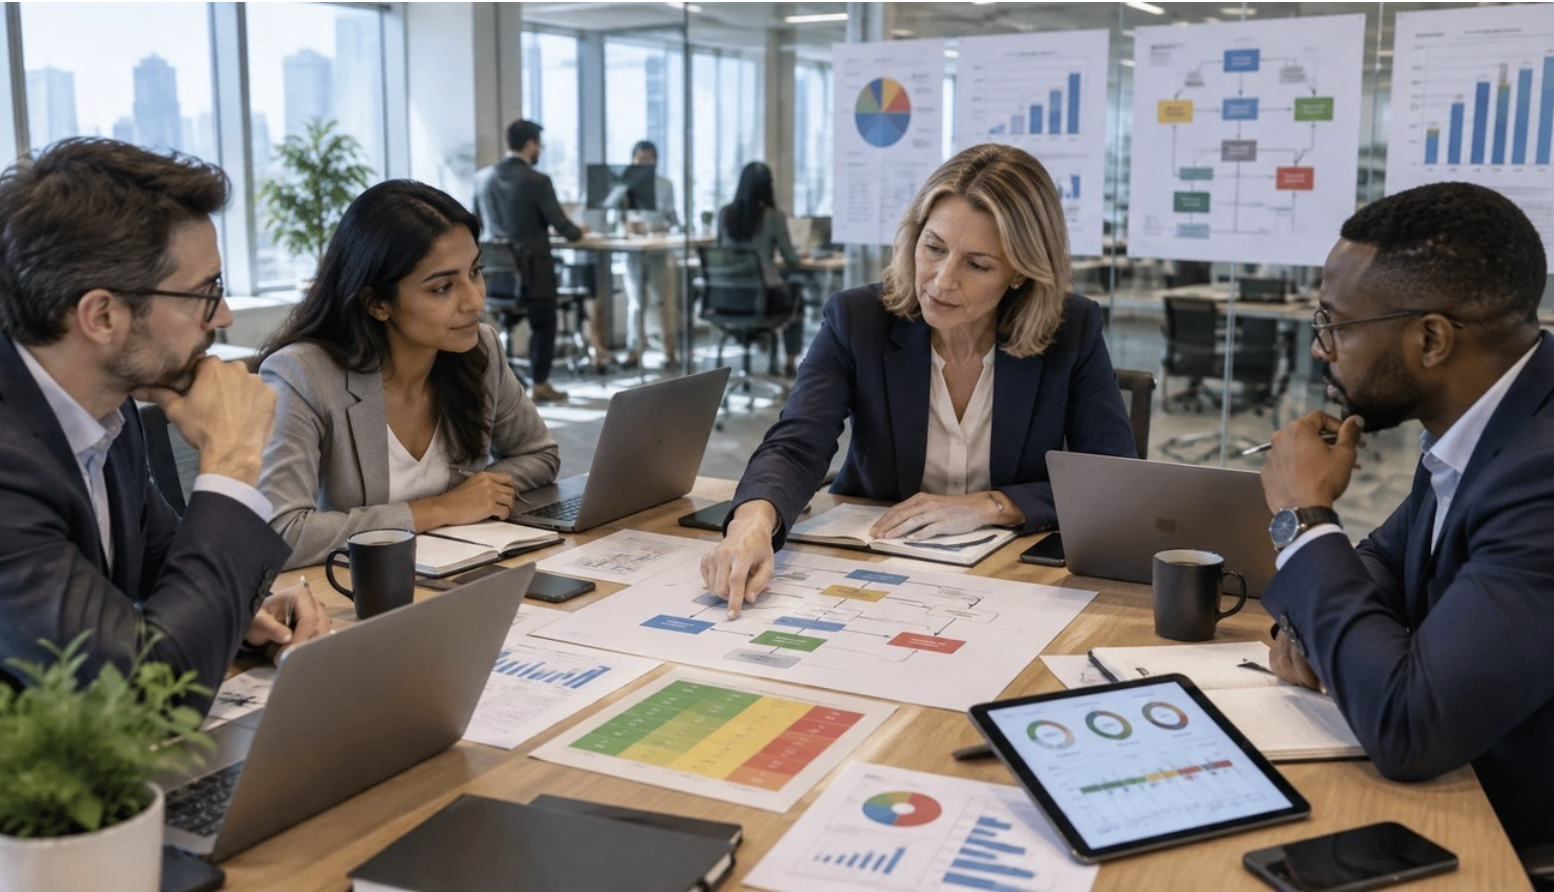
Organizations are prioritizing risk management more than ever. In fact, 57% of key risk officers plan to increase their annual spend on risk monitoring processes to address diverse risk scenarios, such as potential data breaches and loss of customer trust[8]. A risk management framework provides a templated set of guidelines, references and best practices that organizations use to identify, review and eliminate risks in categories of all types[8]. This piece will explore the core components and controls that make up strong risk management strategies. We'll get into leading frameworks, including the NIST Risk Management Framework and ISO 31000 Risk Management Framework[9], and provide implementation strategies and best practices to strengthen your enterprise risk management framework for 2026.
Core Components and Essential Controls of Risk Management Frameworks
A strong risk management framework has seven interconnected components that work together to protect organizational objectives[1]. Risk identification is the foundation. We pinpoint and document potential threats through analytical approaches that include historical data review, industry measures, and professional judgment[1]. This creates a complete risk inventory that informs all subsequent activities.
Risk assessment and analysis follows. We assess each identified risk for likelihood of occurrence and severity of consequences[1]. Quantitative inputs such as loss data and statistical modeling combine with qualitative inputs like expert judgment to produce a prioritized risk portfolio. Risks are ranked by their combined likelihood and impact scores. We often plot them on risk matrices or heat maps and then assess them against risk appetite to determine which require treatment[1].
Risk mitigation translates assessment outputs into action. We make treatment decisions for risks that exceed tolerance thresholds: avoid by eliminating the activity, reduce through controls that lower likelihood or impact, transfer via insurance or contracts, or accept with documented rationale[1]. Treatment plans are assigned to named owners with defined timelines and tracked through completion.
Monitoring functions as a continuous, structured activity rather than a periodic checkpoint[1]. Key risk indicators are tracked against thresholds and trigger escalation when metrics approach limits. Communication will give stakeholders the risk information they need, while governance structures, policies and procedures line up risk management activities with organizational goals and regulatory requirements[1].
Leading Risk Management Frameworks and Their Control Structures
Several frameworks provide structured approaches to organizing risk management activities. COSO updated its Enterprise Risk Management Framework in 2017 and moved focus toward integrating risk with strategy and performance through five interrelated components: Governance and Culture, Strategy and Objective-Setting, Performance, Review and Revision, and Information, Communication and Reporting[2]. Organizations apply these components through 20 principles, whatever their size or sector[2].
Published in 2009 and revised in 2018, ISO 31000 risk management framework organizes around three core elements: principles that define attributes of risk management that works, a governance framework that establishes leadership's commitment and integration, and a process covering identification through monitoring[3]. ISO 31000 functions as guidance rather than a certifiable standard[4].
NIST risk management framework provides a seven-step process: Prepare, Categorize, Select, Implement, Assess, Authorize, and Monitor[5]. Originally designed for federal information systems, the framework applies a risk-based approach to control selection that many private sector organizations have adopted[6].
COBIT 2019 separates governance from management in five domains, with 40 governance and management objectives spanning Evaluate, Direct, and Monitor (EDM); Arrange, Plan, and Organize (APO); Build, Acquire, and Implement (BAI); Deliver, Service, and Support (DSS); and Monitor, Evaluate, and Assess (MEA)[7].
Implementation Strategies and Best Practices for 2026
Successful implementation begins with establishing a risk-aware culture where every employee understands their role in managing uncertainty. Top-level commitment is required to build this culture. Senior leaders must integrate risk considerations into strategic decisions and set an example for others to follow. When senior leaders discuss risk appetite with transparency and make risk-conscious choices, they create an environment where risk management becomes part of everyday routines rather than a compliance exercise.
Documentation is the operational backbone of your risk management framework. We develop policies that clarify responsibilities and establish consistent decision-making processes. These policies define escalation pathways when risks exceed tolerance thresholds. The policies connect to procedures that embed risk assessment into business functions, from procurement and project management to product development. We maintain risk registers that capture identified threats, assigned owners, treatment plans, and review schedules. Updates happen at least quarterly or when most important context changes occur.
Training programs give staff the knowledge to identify, assess, and report risks specific to their roles. This education extends beyond the original onboarding to include annual refreshers and role-specific modules that translate abstract risk concepts into practical actions. Technology platforms centralize risk data and automate workflow escalations. They provide dashboards that track key risk indicators against defined thresholds. Up-to-the-minute detection of emerging threats becomes possible through continuous monitoring capabilities. These insights feed back into assessment cycles and treatment plan adjustments for sustained effectiveness.
Conclusion
We've explored the core components that are the foundations of effective risk management frameworks, got into leading standards including NIST, ISO 31000, COSO, and COBIT, and outlined practical implementation strategies for 2026. You now have a detailed roadmap to build or strengthen your organization's risk management approach. These frameworks protect organizational objectives and enable informed decision-making in an uncertain business environment when implemented with strong governance, continuous monitoring, and risk-aware culture.
References
[1] - https://www.metricstream.com/learn/risk-management-framework-and-components.html
[2] - https://www.konfirmity.com/glossary/coso-enterprise-risk-management-framework
[3] - https://www.metricstream.com/learn/iso-31000-framework-guide.html
[4] - https://www.iso.org/standard/65694.html
[5] - https://csrc.nist.gov/projects/risk-management
[6] - https://www.cybersaint.io/blog/six-steps-of-the-nist-risk-management-framework
[8] - https://www.vanta.com/collection/grc/risk-management-frameworks
[9] -https://www.sentinelone.com/cybersecurity-101/cybersecurity/what-is-risk-management/








Ready to Save Lives at Work?
With Impress Solutions, you’re not just getting a service, you’re securing peace of mind with a partner you can trust. Book a free consultation today, and let’s map out how we can help you save lives at work.

